ID.me Authenticator

Screenshots
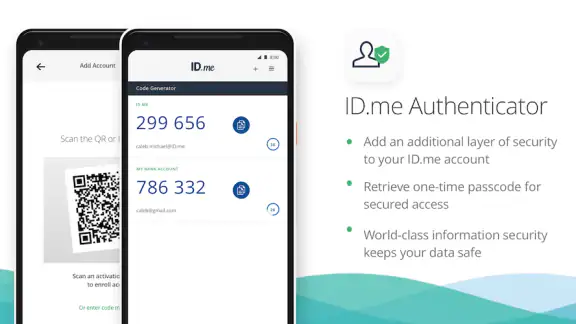
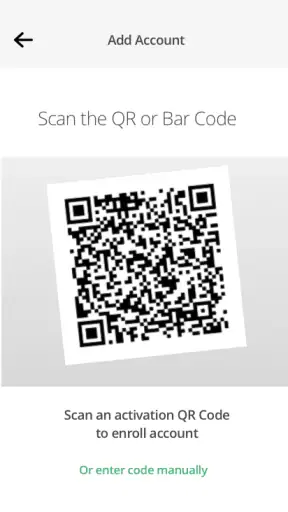
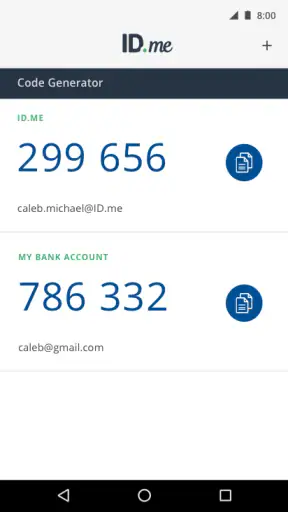
Details
- Rating
- 11.33K reviews
- Version
- 1.12.0-2025082916
- Developer
- ID.me
Analysis by Norviv
I approached ID.me Authenticator as a practical security tool rather than an app I would open every day for entertainment. Its purpose is straightforward: it adds a second verification step when a supported account asks for more than a password. In my experience, that narrow focus is its biggest strength. The app is free, made by ID.me, and sits in the productivity category, but its value really appears at the moment a login needs an extra layer of protection.
The basic idea is easy to understand. A password can be stolen, reused, or exposed, while a second factor makes account access harder for someone who only has that password. ID.me Authenticator is designed to provide that extra factor without turning the process into a large, complicated security project. That makes it appealing to people who want a simple starting point, especially if they already use an ID.me account or encounter ID.me verification while accessing an online service.
There is also a useful accessibility question here: can someone with different visual, motor, sensory, or situational needs complete the authentication process without unnecessary confusion? The answer is mixed. The app keeps its purpose focused, which reduces cognitive load, but authentication itself can still create pressure when a code expires, a phone is unavailable, or a person has difficulty reading small interface elements. I found that the app is easiest to recommend when the user prepares for those moments before an urgent login is required.
How the app reads and guides you through authentication
The interface benefits from doing one job. A dedicated authenticator does not need a news feed, social timeline, shopping area, or a long list of unrelated tools. That limited scope is helpful for people who prefer a predictable screen and for anyone who finds crowded apps tiring to navigate. When I think about readability, the most important advantage is not visual decoration; it is the fact that the app’s purpose is immediately clear.
For a new user, the main challenge is understanding the difference between a password and a second factor. The app itself is only one part of that process, so the surrounding account setup matters. I would not install it just before an important deadline and expect the first attempt to be effortless. A calmer approach is to set it up while already signed in, follow the account’s security instructions carefully, and complete a test login before relying on it.
The app’s current version is 1.12.0-2025082916, and it supports Android 6.0 or newer. That broad operating-system reach is useful for people who keep an older phone instead of upgrading frequently. It does not automatically mean every older device will feel equally comfortable to use, though. Screen quality, text rendering, touch responsiveness, and system settings can vary considerably between phones that meet the same minimum requirement.
I also appreciate that the service is not presented as a complicated enterprise security console. For a person who simply wants two-factor authentication, a smaller learning curve is a real benefit. The trade-off is that a focused app may offer less hand-holding than a broader password manager with setup wizards, password storage, recovery planning, and security education in one place.
Stories Picked for You

Life360 Works Better When Your Household Agrees on What to Share

YouVersion Bible Fits Scripture into Everyday Phone Routines

Matchington Mansion Review: Match-Three Puzzles With a Place to Restore

Android Auto Shows Why Safer Driving Software Does Less

Google Find Hub Runs on Shared Devices and Quiet Trust

Sygic GPS Navigation: The Ultimate Offline Travel Companion
One practical reading tip is to avoid rushing through the first setup screen. Authentication enrollment often involves moving between the account you are protecting and the authenticator on the phone. If you use larger system text, display magnification, or a screen reader, make those adjustments before beginning. That gives you a better chance of noticing instructions and confirmation messages instead of trying to change the phone’s presentation halfway through the process.
Why a simple screen can still demand careful attention
Simple does not always mean effortless. Security screens often use short labels, temporary codes, or prompts that assume the user already understands what is happening. Someone new to two-factor authentication may wonder whether the app is asking for a password, generating a code, or approving a login. I would explain the workflow in plain language before handing the phone to a less confident user: the account asks for extra proof, and the authenticator supplies or confirms that proof.
This distinction matters for older adults, people with cognitive disabilities, and anyone using a phone under stress. A familiar routine helps. I recommend keeping the app in a consistent place on the home screen, learning what its authentication prompt looks like, and avoiding unnecessary changes to the phone’s layout after setup. Those are small decisions, but they reduce the number of choices made during a time-sensitive sign-in.
The app has an Everyone content rating, which fits its serious, general-purpose role. That rating says little about individual usability, so I would still judge it according to the person using it. A user who can comfortably read and tap a standard phone interface may find the experience uncomplicated. A user who needs very large controls, highly customized contrast, or extensive spoken guidance should test the complete login journey rather than judging the app from its store description alone.
Motor, visual, and sensory considerations in real use
Two-factor authentication can be physically demanding in ways that are easy to overlook. A typical login may require holding one device, switching between screens, entering a code, and correcting mistakes if a digit is misread. Someone with tremors, reduced dexterity, limited reach, or one-handed use may find that sequence more tiring than a password manager’s autofill flow. The app’s focused design helps keep the task contained, but it cannot remove the physical demands of using a touchscreen.
If tapping accurately is difficult, I would prepare the phone before the login rather than waiting for a code request. Keep the device charged, unlock it in advance when appropriate, and place it on a stable surface. These steps do not change the software, but they can make the interaction less frustrating. They are particularly useful for users who cannot comfortably hold a phone and type at the same time.
For people with low vision, the main question is whether the text, code, and prompts remain usable with the phone’s own display settings. Larger text and magnification may improve reading, but they can also cause content to occupy more space. That is why I would test the whole process with the preferred settings enabled. A screen that looks fine at the default size may become awkward when enlarged, while a user who needs magnification may be perfectly comfortable after learning where each control appears.
Color should not be the only clue during authentication. If a message changes appearance, the wording should still explain whether the action succeeded, failed, or needs attention. I would pay close attention to written status messages and not rely only on visual changes. This is a good general habit for users with color-vision differences, but it also helps anyone checking the phone in poor lighting.
For people who are deaf or hard of hearing, a visual confirmation is especially important. A phone may be in silent mode, inside a bag, or across a room, so relying on an audible alert is not a dependable workflow. I would keep the app visible during the login and look for the on-screen result. That approach is also better in shared spaces where sound is inconvenient or privacy matters.
Sensory load can come from the situation rather than the interface. A person may be trying to authenticate in a noisy station, a bright public building, a moving vehicle, or a crowded waiting room. In those conditions, copying a temporary code or responding to a prompt becomes harder. I would avoid setting up the app in those environments and complete enrollment somewhere quiet, with enough time to read every instruction.
A useful workflow for people who switch devices or locations
One of the less obvious trade-offs is that an authenticator ties part of the login routine to a physical device. That is convenient when the phone is nearby, but it becomes a barrier when the phone is lost, damaged, uncharged, left at home, or difficult to operate. Before depending on the app, I would review the recovery choices offered by the protected account and make sure I understand how to regain access if the phone cannot be used.
This is not a reason to avoid two-factor authentication. It is a reason to treat recovery as part of setup. A person with mobility limitations may not be able to visit a service center quickly. Someone who travels for work may be separated from another device. A caregiver may assist with normal logins but not be present during an emergency. Planning for those situations is more important than simply installing the app.
For a household supporting an older relative, I would recommend practicing one complete sign-in together. The helper can observe where the user hesitates: opening the app, identifying the correct account, reading the prompt, entering the code, or returning to the original login screen. That observation is more valuable than assuming the app will be easy because it has few visible features.
Where it fits beside other authentication choices
ID.me Authenticator makes the most sense for someone who wants a dedicated, free two-factor tool and does not need a full password-management system. A password manager may be better for a person who wants passwords, passkeys, secure notes, and authentication codes managed in one place. A hardware security key can be a stronger fit for someone who wants a physical device and is comfortable carrying it, although that introduces its own risk of loss and its own learning curve.
Text-message verification can feel easier because it uses a familiar messaging channel, but it is not the same kind of security arrangement as an authenticator app. I would not choose an option only because it feels familiar; I would consider the account’s supported methods, the user’s ability to access the phone, and the recovery process. For some people, the best method is the one they can reliably use without asking for assistance every time.
Compared with a general authenticator that serves many unrelated accounts, this app may feel more approachable if your main goal is a focused ID.me login routine. On the other hand, someone managing numerous accounts across different services may prefer a single authenticator with a broader organizational system. The right choice depends less on which app has the shortest description and more on how many accounts you need to protect and how often you change phones.
The app has reached over five million installs and carries an average rating of 3.5 from around seventy-three thousand ratings, with roughly eleven thousand written reviews. Those figures suggest a substantial user base, but they should not replace personal testing. Authentication problems are highly dependent on the account, phone, network, and recovery path involved. I would treat the app’s popularity as reassurance that it is an established option, not as proof that every user will experience the same setup.
It is free, which removes a financial barrier for people who need a basic second-factor tool. That matters for students, families, and users who cannot justify another subscription. Free does not mean frictionless, however. The real cost may be time spent understanding recovery, moving between screens, or getting help when the phone is unavailable. For accessibility, that time cost can be more significant than the download price.
Situational access: when the small details matter most
Consider a realistic situation: I am trying to sign in to an ID.me-supported service from a library computer while my phone is in a bag. The password works, but the extra verification step appears. If I can reach the phone, unlock it, read the prompt, and return to the computer without losing track of the process, the app does its job quietly. If the phone battery is low or the screen is difficult to read under harsh lighting, the same security step becomes a serious interruption.
That example shows why I would not describe the app as universally accessible simply because the interface is simple. Access depends on the complete chain: the website, the phone, the account settings, the person’s abilities, and the environment. A person with limited vision may be comfortable at home but struggle in sunlight. Someone with limited hand movement may manage one-handed use at a desk but not while standing in a queue. Someone with anxiety may need a rehearsed routine to avoid freezing when a code request appears.
Travel creates another consideration. If you change phone numbers, replace the device, or use a different network, authentication can become more complicated even when the app itself has not changed. I would update account recovery details before traveling, keep the phone accessible, and avoid deleting the old setup until the new arrangement has been tested. That is particularly important for users who rely on a family member, interpreter, support worker, or trusted assistant during account recovery.
Shared devices also deserve caution. A phone used by several people can make it unclear whose account is being authenticated. I would avoid casual sharing of the app and make sure the person approving a login knows which account the request belongs to. This is both a privacy matter and an accessibility matter: confusion increases when multiple people have different routines, permissions, or support needs.
For users with intermittent internet access, I would test authentication in the exact environment where it will be needed. The app may be installed, but the complete login still involves the service being accessed and the phone’s ability to communicate as expected. A successful setup at home does not guarantee an equally smooth attempt from a rural location, basement, airplane, or crowded public network.
Remaining barriers I would want users to plan around
The largest barrier is dependence on a phone. If the phone is lost, stolen, broken, locked, or inaccessible because of a disability-related issue, the second factor may stop being convenient. The solution is not to weaken account security casually; it is to understand the account’s recovery route before a crisis. I would save recovery information in a secure, accessible place and make sure a trusted helper knows how to assist without receiving unnecessary passwords.
Another barrier is the gap between technical security and human confidence. A user may worry that approving the wrong request will expose an account, or may approve a prompt without understanding it simply to make the screen disappear. Clear personal rules help: authenticate only when you initiated the login, stop if the request is unexpected, and ask for help when the account or device behaves differently than usual.
People who need screen readers or specialized input should test their actual device and operating-system settings. I would not promise that every control, label, or temporary authentication element will behave perfectly with every assistive technology. The responsible approach is to try the app during a low-stakes login and keep an alternative recovery method available. That is not a criticism unique to this product; it is a necessary precaution for any security tool that sits between a user and an important account.
There is also a support barrier. When authentication fails, the user may not know whether the problem comes from the app, the protected website, the account configuration, the phone, or the network. A person who struggles with technical troubleshooting may need another person to identify the failing step. I would record the sequence in simple terms—where the login stopped, what message appeared, and whether the app opened—without recording the secret code itself.
Finally, the app is not the right choice for someone who wants a complete digital-security suite. It does not replace a password manager, safe password habits, device updates, or a recovery plan. Someone managing many accounts may find a broader authenticator more efficient, while a high-risk user may prefer a hardware-based method. ID.me Authenticator is best understood as a focused component, not a complete answer to every security and accessibility problem.
My inclusive verdict after weighing convenience and control
I see ID.me Authenticator as a sensible option for people who want a free, dedicated way to add two-factor authentication to an ID.me login routine. Its narrow purpose makes it less intimidating than a large security suite, and its support for Android 6.0 or newer gives people with older phones a chance to use it. The fact that it is rated for Everyone also matches its general-purpose audience.
My recommendation comes with preparation attached. Set it up when you have time, test the complete login, adjust the phone’s text and display settings first, and plan what happens if the phone cannot be used. Those steps are especially important for people with low vision, limited dexterity, hearing differences, cognitive disabilities, or changing access needs. They also help anyone who logs in from public, noisy, bright, or unreliable environments.
The app is most inclusive when it is treated as part of a prepared workflow, not as a magical fix for every access problem. I would recommend it to a user who values a straightforward authenticator and can keep the phone available during sign-in. I would steer a person who needs extensive accessibility customization, manages many unrelated accounts, or cannot reliably access one phone toward testing a different authentication method as well.
Overall, I like the restraint of the product. It does not need to do ten things to be useful, and that simplicity can reduce confusion at an important moment. At the same time, security always introduces a little friction, and this app cannot remove the practical problems of device dependence, temporary codes, recovery, or environmental distractions. If you understand those trade-offs and prepare before you need it, ID.me Authenticator is a reasonable productivity tool for strengthening everyday account access.
Frequently Asked Questions
01What is ID.me Authenticator and what is it used for?
ID.me Authenticator is a security app that helps protect your ID.me account with multi-factor authentication. After signing in with your username and password, you may be asked to approve a notification or enter a time-based verification code generated by the app. It is commonly used when accessing government services, benefits, healthcare portals, education services, and other websites that support ID.me.
02How do I set up ID.me Authenticator on my Android or iPhone?
After installing the app, sign in to your ID.me account through a supported website or the ID.me sign-in page and choose the option to set up an authenticator app. Scan the displayed QR code with ID.me Authenticator, or enter the setup key manually if scanning is unavailable. Complete the verification step, then save any recovery codes provided during setup in a secure location.
03Does ID.me Authenticator work without an internet connection?
The app can generally generate time-based security codes without an active internet connection, which is useful when cellular data or Wi-Fi is unavailable. However, some account actions, sign-in pages, push notifications, or identity-verification processes may still require internet access. Your phone’s date and time should also be set automatically, because an incorrect clock can cause otherwise valid codes to be rejected.
04What should I do if I lose my phone or cannot access the app?
If your phone is lost, replaced, damaged, or unavailable, use another verification method offered by ID.me, such as backup codes, text-message verification, email, or an approved identity-verification recovery process. If you are still signed in on a trusted device, review your account security settings and remove the old authenticator. Never share recovery codes, and contact ID.me Support through its official website if you cannot regain access.
05Is ID.me Authenticator safe, and what permissions does it require?
ID.me Authenticator is designed to add an extra security layer rather than replace your ID.me password or identity verification. It may request permission for camera access when scanning a QR code, while notification access can be needed for approval prompts. Download it only from the official Google Play Store or Apple App Store, keep your device updated, use a screen lock, and avoid installing unofficial copies.


